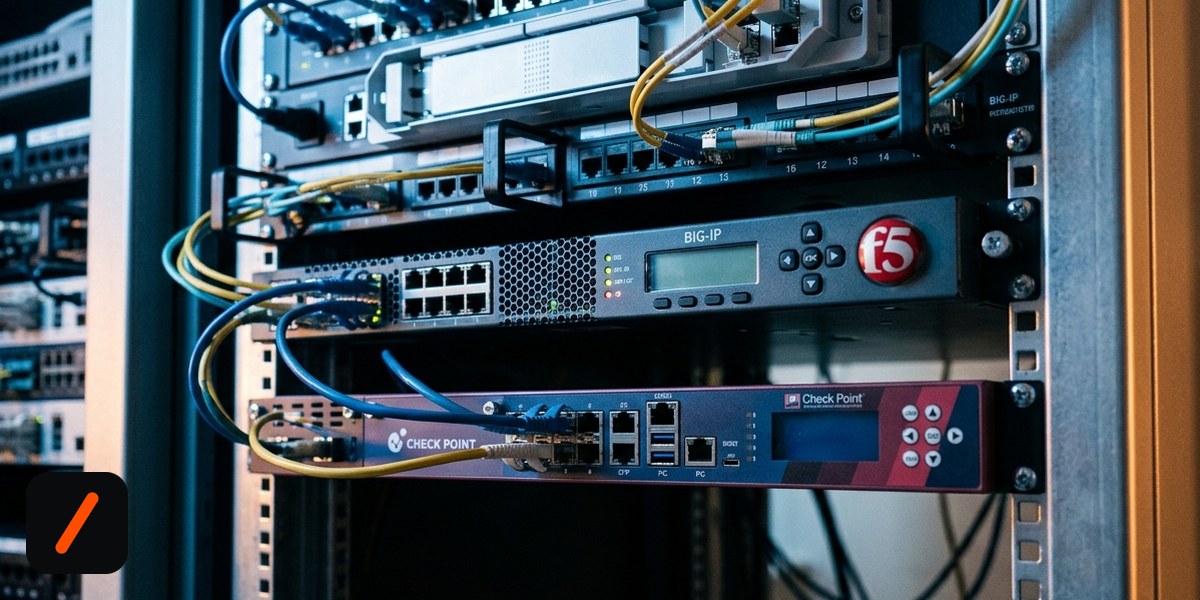
CISA added four vulnerabilities to its Known Exploited Vulnerabilities catalog on September 22, 2026, and two of them sit inside the boxes guarding the edge of nearly every enterprise network: F5's BIG-IP Access Policy Manager and Check Point's Security Gateway. Civilian federal agencies had three days to patch, a deadline that's already passed. If you run either product, the question isn't whether to patch. It's what order.
- CISA's September 22 batch added CVE-2026-94127 (F5 BIG-IP APM), CVE-2026-85102 and CVE-2026-93616 (both Check Point), and CVE-2026-93952 (Arista VeloCloud Orchestrator).
- Check Point's management path traversal was reportedly exploited starting July 23, more than two months before it reached CISA's list.
- The F5 flaw only exists on a virtual server that pairs an APM access policy, an OAuth profile, and APM set as the OAuth Authorization Server.
- Federal agencies had until September 25 under Binding Operational Directive 26-04. Treat that as the outer bound, not the target.
Why did two unrelated vendors land in the same KEV batch?
F5 and Check Point don't share code or customers. They share a role: both terminate VPN and access-policy traffic at the perimeter before it reaches anything internal, and both have been through this before. SonicWall's SMA1000 took its third zero-day chain in a year recently; Citrix NetScaler shipped two unpatched RCEs around the same stretch. A working exploit at the edge skips past every internal control a company built assuming the perimeter already did its job. The fourth CVE in this batch, CVE-2026-93952 in Arista's VeloCloud Orchestrator, is an improper input validation flaw sitting in the same category, an internet-facing SD-WAN management plane, and it will likely get less attention than it deserves.
RelatedZimbra RCE Flaw Under Active Attack, CISA Gives Feds 3 Days
Which BIG-IP setups can actually be hit by CVE-2026-94127?
It's a heap-based buffer overflow, CVSS 9.8 under v3.1 and 9.3 under v4.0, that lets an attacker send crafted traffic to an affected OAuth configuration and get unauthenticated remote code execution on the data plane. F5 says it found the defect internally, then observed active exploitation before it had finished shipping a fix. The catch is that it only fires under one specific combination: a virtual server running an APM access policy and an OAuth profile together, with APM acting as the OAuth Authorization Server rather than a Client or Resource Server. Change any of those three conditions and this particular CVE doesn't apply. Affected versions are APM 21.1.0, 17.5.0 through 17.5.1, and 17.1.0 through 17.1.3, including appliance mode; no other F5 line is implicated. F5 published hotfixes and three indicators of compromise with advisory K000162605 on September 22.
How long were the Check Point bugs live before anyone noticed?
CVE-2026-93616 is a pre-auth path traversal in Check Point's management web service that lets an attacker load Java classes and run scripts without credentials. Check Point's advisory says limited, targeted exploitation started July 23, roughly two months before it hit a public exploited-vulnerabilities list. It affects Security Gateway and Management from R80 through R82.20, and Check Point points admins to sk1000117 and sk1000171.
CVE-2026-85102 is newer and louder: a pre-auth RCE, also CVSS 9.8, triggered during VPN certificate negotiation. A fix has existed since September 9, but attackers started using it anyway on September 12, targeting Spark firewall customers globally through VPNs and proxies. The certificates in these attacks carry telltale subjects, CN=vpn, CN=vpn-user, and CN=vpnuser under OU=users, O=global, worth grepping your logs for. Post-exploitation, Check Point has observed internal port and service scanning.
| Vulnerability | F5 BIG-IP APM · CVE-2026-94127 | Check Point Gateway · CVE-2026-85102 | Check Point Mgmt · CVE-2026-93616 |
|---|---|---|---|
| Flaw type | Heap-based buffer overflow | Improper certificate validation | Path traversal |
| CVSS v3.1 | 9.8 | 9.8 | 9.8 |
| Authentication | None | None, VPN negotiation | None, management service |
| Exploited since | Disclosed Sep 22 | Sep 12, 2026 | Jul 23, 2026 |
| Condition | APM + OAuth profile + Authorization Server role | Gateway/Spark, VPN enabled | Management service reachable |
| Fix | Hotfix, K000162605 | Available since Sep 9 | sk1000117 / sk1000171 |
How did the attack timeline actually unfold?
- Jul 23, 2026Check Point path traversal exploitation begins. CVE-2026-93616, limited and targeted, not yet disclosed.
- Sep 9, 2026Check Point ships a fix for the VPN flaw. CVE-2026-85102 patch available, three days early.
- Sep 12, 2026CVE-2026-85102 exploitation begins. Spark customers targeted globally via VPNs.
- Sep 22, 2026CISA adds all four CVEs to KEV. F5 publishes K000162605 the same day.
- Sep 25, 2026Federal remediation deadline passes. Three days, under BOD 26-04.
What order should you patch in this week?
Sort by what the internet can reach, then by how long it has been under attack. CVE-2026-85102 goes first: it sits on the VPN gateway, which is internet-facing by design, it needs no credentials, attackers have been hitting it since September 12, and the fix has existed since September 9, so there is no reason it is still open. While you are in there, search your VPN logs for the vpn, vpn-user and vpnuser certificate subjects. CVE-2026-93616 comes next, patched through sk1000117 or sk1000171. It has the longest exploitation history, roughly two months against the management plane, but the Management web service should not be reachable from the internet; if yours is, move it to the top of the list and treat the box as suspect. Then F5. Confirm whether the specific condition, APM plus an OAuth profile plus the Authorization Server role, actually applies before deciding how urgent CVE-2026-94127 is for you. If it applies, patch through K000162605 now and check F5's three published IoCs; if it does not, the hotfix can ride your normal cycle. Do not skip Arista's VeloCloud Orchestrator just because it is quieter. CVE-2026-93952 rode into KEV the same day as the other three.
RelatedCisco Email Gateway Root Bug Exploited, CISA Gives 3 Days
- Scan for the known VPN certificate subjects. CN=vpn, CN=vpn-user and CN=vpnuser under OU=users, O=global mean someone tried. Check what that session did next, since post-exploitation here starts with internal port and service scans.
- Don't judge F5 exposure by CVSS alone. Two admins can read the same advisory and reach opposite, both wrong, conclusions.
- Arista deserves the same urgency. CVE-2026-93952 landed in the same batch and manages the same kind of internet-facing plane.
- Expect this cadence to continue. SonicWall, Citrix, F5 and Check Point have each disclosed exploited edge flaws within weeks of one another this autumn.
Our take
The F5 bug is the more interesting failure mode, not because it's more dangerous, but because config-dependence cuts both ways and both directions are wrong: skim the CVSS score and you'll waste a week chasing a non-issue, or read "OAuth Authorization Server" and assume it's someone else's setup, and you'll skip a patch you actually needed. Check Point's problem is simpler and worse. Two months of quiet exploitation before anyone outside the company noticed makes a three-day patch deadline feel almost beside the point; the clock that mattered had already been running for weeks before CISA started its own.
None of this is new. It is not the first time this year a perimeter appliance vendor has shipped a fix chasing exploitation already underway, and the pattern is familiar enough to plan around: assume the edge boxes are the first thing attackers try, verify your actual configuration instead of trusting a headline CVSS number, and check for the specific indicators vendors publish instead of waiting for a dashboard to turn red.
- OfficialCISA KEV alert, Sep 22 2026 , the four-CVE addition
- VendorF5 advisory K000162605 , CVE-2026-94127 details
- VendorCheck Point security advisory , both CVEs
- ResearchRapid7 ETR , technical breakdown
- CoverageBleepingComputer , on the VPN RCE
- LiveCVE watchlist , what we track as exploited
Original analysis by GenZTech. Source: CISA.