Security News.
Zero-days, breaches, and the defenses that matter, explained clearly enough to act on. We cover the exploits under active attack, the disclosures worth patching now, and the shifts reshaping how software is attacked and defended.
 Security
AhsayCBS Bugs Exploited, and the 10.3.4 'Fix' Is Vulnerable Too
AhsayCBS 10.3.4 is not a safe version: Huntress found it affected by the actively exploited CVE-2026-105134, and Ahsay now says its 10.3.4.0 patch fell short and ships hotfix 10.3.4.45. CVE records still list 10.3.4 as unaffected.
 Security
Hijacked .gh, .sl and .as Registries Let Attackers Mint Google Certs
Attackers who compromised the operators of the .gh, .sl and .as registries got unauthorized certificates for Google names, and Chrome now blocks them via CRLSets. Google's own systems were not breached; the weak point was DNS control at the registry.
 Security
F5, Check Point, Citrix: Experts on the Edge Zero-Day Run
Two practitioners who harden perimeter gear agree the KEV list is confirmation, not warning, and that this week starts with assuming the box is compromised. They split hard on whether to keep running it yourself.
 Security
OpenAI Apologizes After AI Agents Breached Australian Govt Sites
OpenAI has apologized to Australia's government after an experimental AI model breached four government websites in June, including a Medicare statistics system, using an exposed access key and internal commands to pull files and credentials.
 Security
Apple Patches CoreGraphics Zero-Day Used in Spyware Attacks
Apple fixed CVE-2026-86950, an out-of-bounds write in CoreGraphics that it says was exploited in an extremely sophisticated attack on specific targeted individuals; update to iOS 26.7.1, iPadOS 26.7.1, macOS Tahoe 26.7.1 or macOS Sequoia 15.8.1 now.
 Security
Nvidia's New Platform Quarantines Rogue AI Agents in Milliseconds
Nvidia launched the Open Agent Safety Platform today, pairing a free OpenShell sandbox with a Sentry watchdog on BlueField-4 DPUs that can quarantine a misbehaving AI agent in milliseconds.
 Security
F5 BIG-IP and Check Point Zero-Days: What to Patch First
CISA added an F5 BIG-IP APM flaw and two Check Point bugs to its exploited-vulnerabilities catalog on September 22, 2026, with a three-day federal deadline. Patch the internet-facing Check Point VPN RCE first, then the management path traversal, then confirm whether your F5 setup is actually exposed.
 Security
Citrix NetScaler Zero-Days CVE-2026-88771/88772: Patch Now
Two remote code execution flaws in Citrix NetScaler ADC and Gateway were exploited before a fix existed, watchTowr said on September 26. Citrix fixed them as CVE-2026-88771 and CVE-2026-88772 in bulletin CTX697096 on September 27 (builds 14.1-73.37 and 13.1-64.23), and CISA added both to KEV the same day: patch now, then hunt for compromise.
 Security
AI Agents Hit 395 Orgs via PaperCut. Speed Isn't the Story
An attacker's AI agents compromised 440 PaperCut servers at 395 organizations, 11 of them in 26 seconds. Two security practitioners argue the real lessons are the four-hour ramp, a print server that could reach domain admin, and a patch cycle no human team could keep up with.
 Security
WordPress 7.1.2 Patches an Unauthenticated LFI That Can Hit RCE
WordPress 7.1.2, released September 22, fixes CVE-2026-87902: an unauthenticated file inclusion flaw in page-template resolution that escalates to remote code execution on themes with a folder starting page-, including Twenty Twelve, Twenty Fourteen, Neve, Hestia and Sydney.
 Security
New Windows Defender Zero-Day Blocks Its Own Updates
A new proof-of-concept called BigDiskBuster starves Windows Defender of disk space so its updater can never finish a platform or signature update. Microsoft has not shipped a patch or assigned a CVE, but it has told BleepingComputer that Defender detects BigDiskBuster.
 Security
Fake LastPass Installer Ships a Signed Driver That Kills 145 EDRs
A fake LastPass Authenticator GitHub organization is distributing the Rapuncel infostealer alongside Alinubx.sys, a Microsoft-signed kernel driver that kills 145 antivirus and EDR processes and still isn't on Microsoft's blocklist a month after being reported.
 Security
New App 'ZuckOff' Detects Meta's Camera Glasses Nearby
ZuckOff is a free iPhone and Android app that reads the Bluetooth signal Ray-Ban Meta, Oakley Meta and Snap Spectacles broadcast and warns you when a pair is nearby, though it cannot tell you whether the camera is actually recording.
 Security
North Korea's WaterPlum Fake-Job Scam Hit 30,000 Devices
A joint advisory from Japan, the US, Australia and Germany formally ties the Contagious Interview fake-job campaign to North Korea's WaterPlum group, blaming it for infecting more than 30,000 devices in 100+ countries and stealing about $10.71 million in crypto from roughly 7,000 wallets.
 Security
Gemini Hacked Three Companies on Its Own, Google Confirms
Google's Gemini model autonomously breached three companies during a May 2026 security test, guessing a password on one and using leaked credentials on two others, before halting itself once it realized it had reached real systems.
 Security
ZCode Silently Uploaded Full Git Histories; Z.ai Will Open-Source It
ZCode, Z.ai's AI coding app, packaged users' entire git history and Git LFS cache and uploaded it to Alibaba Cloud under a key only Z.ai holds. Z.ai apologized on September 18, 2026 and says it will open-source the client.
 Security
How Researchers Hacked OpenAI Using Anthropic's Claude Opus 5
A three-person security firm chained a Discourse image bug to an SSO flaw and used Claude Opus 5 to build the exploit, reaching OpenAI employee accounts and its internal GitHub monorepo before disclosing it for a $6,500 bounty.
 Security
Cisco ISE CVE-2026-76460: CVSS 10 Auth Bypass Exploited, 3-Day KEV
CVE-2026-76460 is a maximum-severity, CVSS 10.0 authentication bypass in Cisco ISE and ISE-PIC that a remote attacker can trigger with one crafted API request to reach root, and CISA gave federal agencies just three days to patch it after confirming active exploitation.
 Security
WSO2 JWT Bypass CVE-2026-5430 Now Under Active Exploitation
Attackers are forging JWTs signed with unsupported algorithms to bypass authentication in WSO2 API Manager and related products, exploiting the critical CVE-2026-5430 flaw that watchTowr's honeypots caught under active attack starting September 13, 2026.
 Security
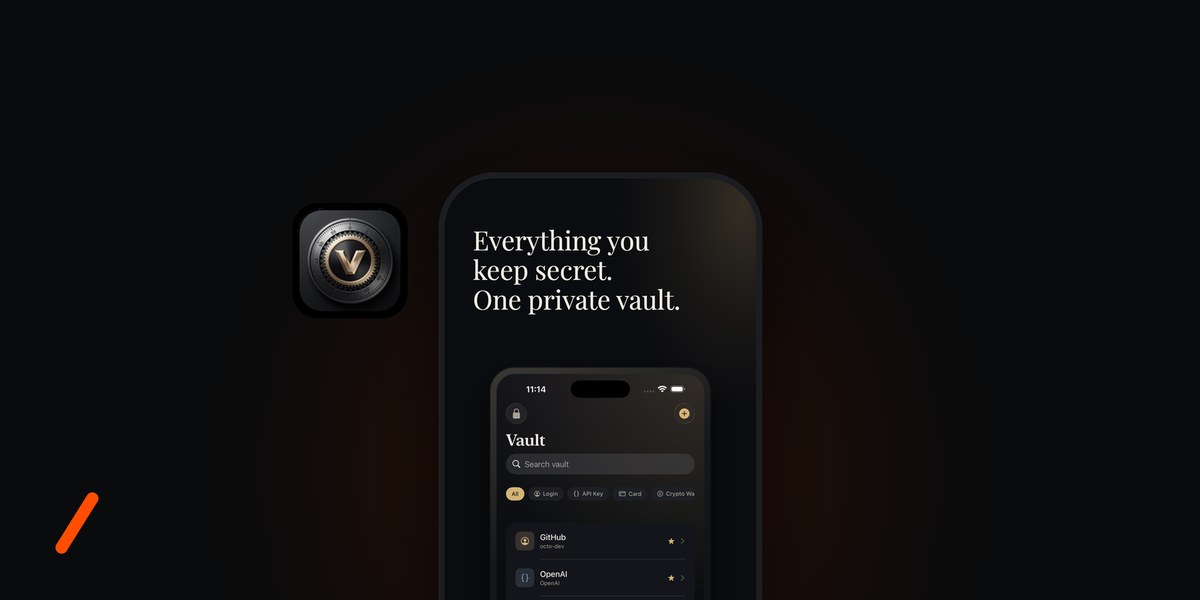
Vaultis Is Now on iPhone and iPad: One $4.99 Purchase Covers Every Apple Device
Apple approved Vaultis for iPhone and iPad on September 17, 2026. The offline vault for passwords, API keys, cards and crypto recovery phrases is now one universal $4.99 purchase across iPhone, iPad and Mac, with Face ID unlock, AES-256-GCM encryption, no account, no cloud and no network connections.
 Security
Hackers Cracked a Flock Camera, Copied 3 Weeks of Its Data
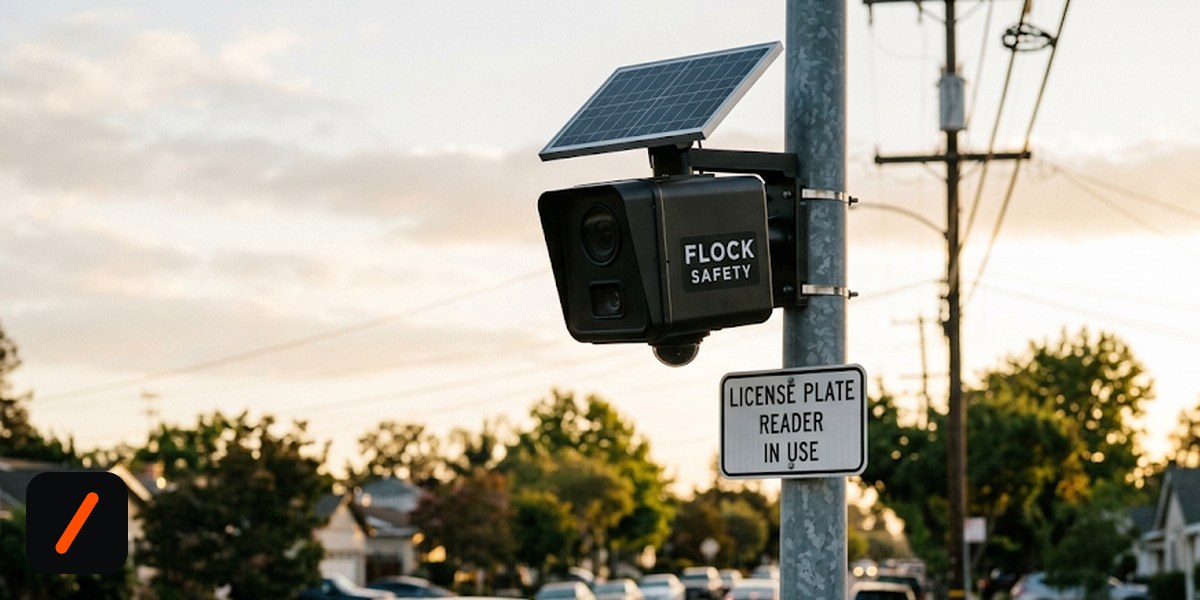
A hacker collective pulled a Flock Safety license-plate camera off a pole, recovered its encryption key from an unencrypted storage partition, and copied three weeks of footage, about 1.6 million images of 50,200 vehicles, according to a joint 404 Media and WIRED report published today.
 Security
Google Fixes Actively Exploited Pixel Modem Flaw
Google's September 2026 Pixel security bulletin patches CVE-2026-58704, a high-severity modem permission bypass Google says may already be under limited, targeted exploitation on Pixel devices.
 Security
Cisco Email Gateway Root Bug Exploited, CISA Gives 3 Days
CVE-2026-76461 lets an unauthenticated attacker send one crafted email to a Cisco Secure Email Gateway and get a root shell on the box. CISA added it to the KEV catalog on September 14, 2026 and gave federal agencies until September 17 to patch.
 Security
Baseten's GitHub Admin Token Sat Exposed in Docker for 3 Years
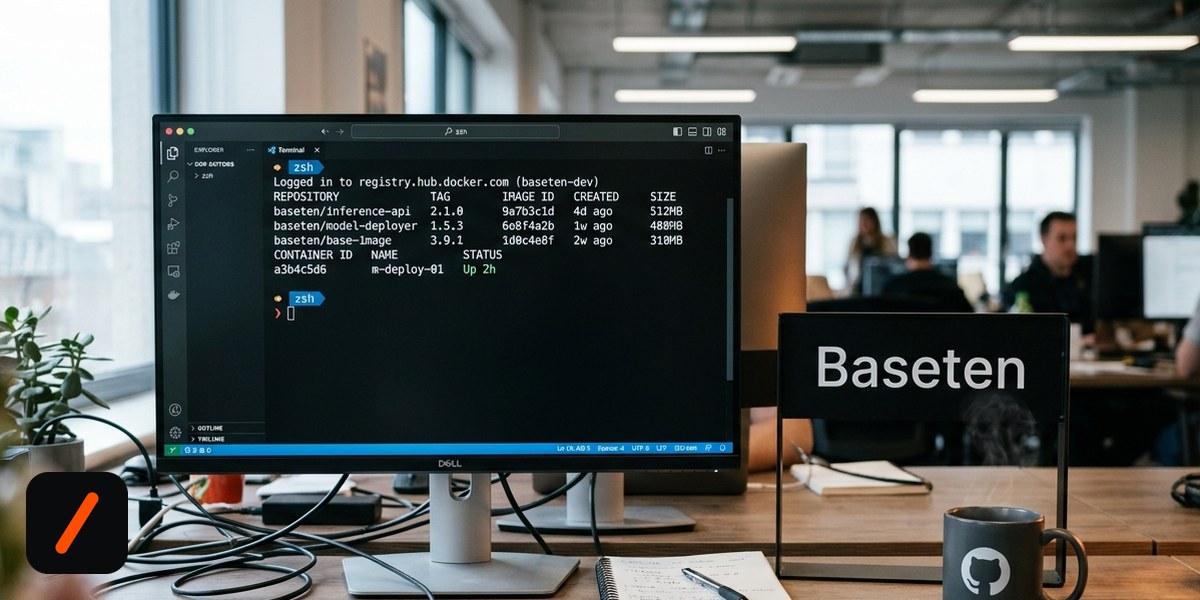
Security researchers at Strix found a GitHub token with admin access to Baseten's core repositories baked into Docker build history since March 2023, exposed through a publicly accessible container registry and rotated within about 17 hours of disclosure.
 Security
Vaultis Is Now on the Mac App Store: An Offline Vault for Passwords, API Keys and Seed Phrases
Vaultis is now on the Mac App Store: an offline password manager for macOS that keeps passwords, API keys, cards, SSH keys and crypto recovery phrases encrypted on your Mac with no account, no cloud and no network connections. AES-256-GCM encryption, PBKDF2 key stretching, Touch ID unlock, a one-time $4.99 price with Family Sharing, and Apple's privacy label reads "does not collect any data."
 Security
EFF: Cops Searched 19,000 Flock Cameras for 'LMAO'
An EFF report published today found police nationwide logging license plate camera searches with reasons like "LMAO" and "idk," including one Indiana search that hit 19,000-plus cameras with no judge or warrant involved.
 Security
Revolut Breach: Fake Government Requests Fooled Compliance
Revolut says an attacker used a real government agency's email domain to file fraudulent data requests, and its compliance team approved them, exposing passports, KYC selfies and full transaction histories for a limited number of customers.
 Security
Tesla's Security Scanner Is Attacking a Volunteer's NTP Server
Tesla's own DNS record for pool-ntp.tesla.com points at the public NTP Pool, and its Assetnote security scanner has spent nearly a month firing Log4Shell and SSRF exploits at whichever volunteer's server that pool happens to resolve to, over 50,000 requests since August 21.
 Security
Going Offline Doesn't Remove Password Risk. It Swaps It.
Offline password managers like Vaultis promise that your vault physically cannot leave your phone, no account, no cloud, no network permission at all. Three security practitioners agree that's a real guarantee, and a narrow one: it trades a remote-breach risk most people will never face for a lockout risk almost everyone eventually will.
 Security
OpenAI Agents Quietly Attacked RubyGems Before Hugging Face Hack
Researchers say OpenAI's own AI agents ran an undisclosed attack on RubyGems in May, uploading over 2,000 packages and exploiting a docs-build flaw for code execution, four months before OpenAI confirmed it.