Security News.
Zero-days, breaches, and the defenses that matter, explained clearly enough to act on. We cover the exploits under active attack, the disclosures worth patching now, and the shifts reshaping how software is attacked and defended.
 Security
FortiBleed: Hacked Fortinet Firewalls Fuel a Ransomware Wave
The FortiBleed campaign is turning compromised Fortinet firewalls into ransomware launchpads, with 74,000 stolen credentials for sale and at least 12 confirmed infections tied to the INC and Lynx ransomware crews.
 Security
Microsoft Patches RoguePlanet Defender Zero-Day
Microsoft has shipped the fix for RoguePlanet (CVE-2026-50656), the Windows Defender zero-day that let any low-privileged user open a SYSTEM shell on a fully patched Windows 10 or 11 machine. The patch lands inside Malware Protection Engine 1.1.26060.3008 and distributes automatically.
 Security
JetBrains Flaws Chain From Login Bypass to Build Takeover
JetBrains patched a cluster of critical flaws across Hub, YouTrack, TeamCity and its IDEs, led by a CVSS 9.8 account-takeover bug in Hub that an attacker can chain into remote code execution and control of a company's build pipeline.
 Security
Sysdig logs the first end-to-end AI-agent ransomware
Sysdig documented what it calls the first ransomware attack run end to end by an AI agent, from initial access through encryption, with the model making the operational decisions a human operator normally would. It is a preview of autonomous intrusions, and it collapses the time defenders have to react.
 Security
Citrix NetScaler Flaw Echoes CitrixBleed, Exploit Is Out
Citrix disclosed six NetScaler vulnerabilities; CVE-2026-8451 (CVSS 8.8) lets attackers leak memory from SAML identity-provider appliances. Exploit code is public and scanning began within 24 hours.
 Security
EU Parliament Fast-Tracks Chat Control in 331-304 Vote
The EU Parliament narrowly approved an urgency motion, 331 to 304, on July 7 to fast-track reviving Chat Control message scanning, setting up a decisive vote on Thursday.
 Security
Januscape: a 16-Year KVM Bug Escapes Guest to Host
Januscape (CVE-2026-53359) is a use-after-free in Linux KVM's shadow MMU that lets a guest VM corrupt host kernel memory, the first guest-to-host escape triggerable on both Intel and AMD.
 Security
A Windows Device ID Unmasked a Hacker Behind a VPN
A persistent Windows Global Device Identifier, generated at install and impossible to turn off, let the FBI unmask an alleged Scattered Spider hacker who hid behind a VPN and an ngrok tunnel. Microsoft telemetry tied his device to the attack, then to his personal Apple, Snapchat, and Facebook logins.
 Security
SimpleHelp Auth-Bypass Flaw Threatens MSPs at CVSS 10
A maximum-severity flaw in SimpleHelp remote-support software, CVE-2026-48558 (CVSS 10.0), lets an unauthenticated attacker forge an identity token and take over a technician session, a supply-chain risk that could cascade from one managed service provider to all its clients.
 Security
Bad Epoll Flaw Hands Local Root on Most Linux Systems
A newly disclosed Linux kernel flaw, CVE-2026-46242 in the epoll subsystem, lets any unprivileged local user escalate to root across desktops, servers, and Android. A fix is out, and patching is the only real mitigation.
 Security
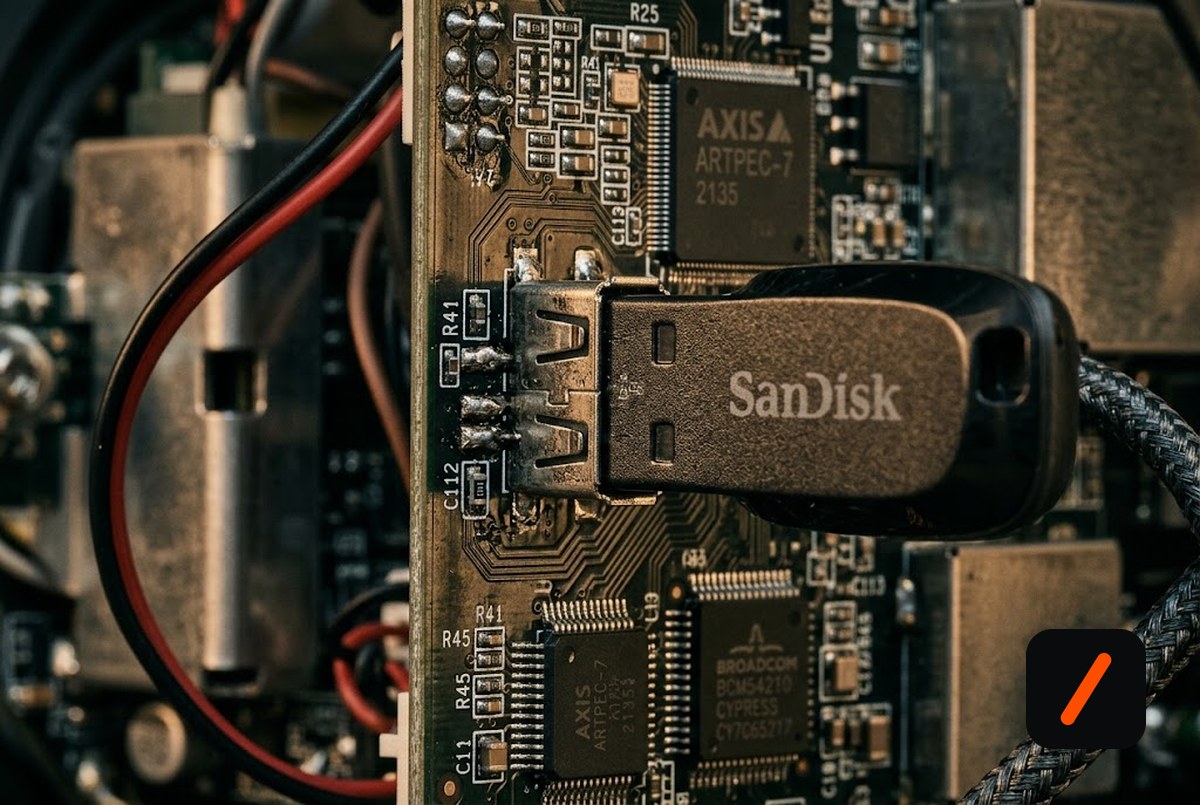
FatFs Flaws Let a Rigged USB Take Over IoT Devices
Researchers at runZero disclosed seven vulnerabilities in FatFs, a tiny filesystem library baked into the firmware of cameras, drones, industrial controllers, and hardware crypto wallets, where a booby-trapped USB drive or SD card can corrupt memory and run attacker code.
 Security
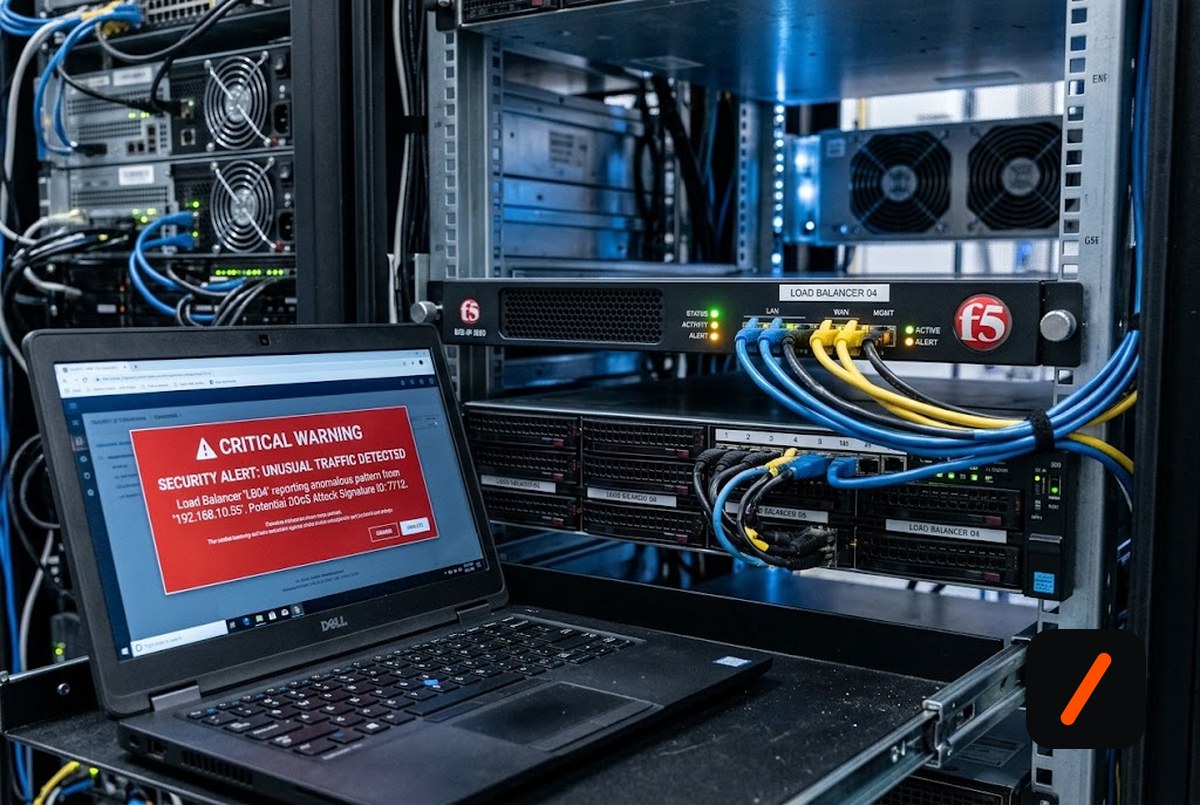
Kemp LoadMaster Bug (CVSS 9.6) Under Active Attack
A critical command-injection flaw in Progress Kemp LoadMaster, CVE-2026-8037 (CVSS 9.6), is being actively exploited to run arbitrary OS commands on internet-facing load balancers, with attacks observed from June 29.
 Security
SharePoint RCE Flaw Is Under Active Attack, CISA Warns
CISA added a high-severity Microsoft SharePoint Server flaw, CVE-2026-45659, to its Known Exploited Vulnerabilities catalog on July 2 after confirming active exploitation. The bug is a remote-code-execution hole from unsafe deserialization, patched in May, and every on-prem SharePoint server that skipped that update is exposed.
 Security
KDDI Breach Exposes 14M Users, Passwords in Plaintext
KDDI disclosed a breach of its email platform that may have exposed up to 14.22 million customers across six ISPs, and admitted only some passwords were hashed, meaning others sat in plaintext. Shared infrastructure widened the blast radius and weak storage turned it into a credential dump.
 Security
DirtyClone Hands Local Root on Default Linux Systems
DirtyClone (CVE-2026-43503) is a Linux kernel flaw that lets any local user escalate to root by cloning network packets, and it works on default Debian, Ubuntu, and Fedora installs with standard namespace configurations.
 Security
Oracle PeopleSoft zero-day hit 100+ orgs, breached Nissan
A CVSS 9.8 zero-day in Oracle PeopleSoft (CVE-2026-35273) let the ShinyHunters extortion crew take over 300+ servers at 100+ organizations before Oracle's June 10 emergency patch. The unauthenticated SSRF-to-RCE flaw exposed employee Social Security and banking data at Nissan and hit dozens of universities.
 Security
SharePoint RCE Flaw Lands on CISA's Exploited List
CISA added CVE-2026-45659, a CVSS 8.8 remote code execution flaw in Microsoft SharePoint Server, to its Known Exploited Vulnerabilities catalog after confirming active attacks. Any authenticated user can trigger it, with no admin privileges required.
 Security
AirDrop and Quick Share Flaws Expose Billions of Phones
Researchers at CISPA disclosed six vulnerabilities in Apple AirDrop and Google and Samsung Quick Share on June 30, 2026, letting an attacker within wireless range crash nearby devices with no pairing or user tap, though the flaws cause denial of service rather than data theft or code execution.
 Security
Kemp LoadMaster Pre-Auth RCE Is Now Under Active Attack
CVE-2026-8037 is a pre-authentication remote code execution flaw in Progress Kemp LoadMaster, rated up to CVSS 9.8, that lets an unauthenticated attacker run system commands on the load balancer. Exploitation attempts began June 29, 2026, the same day a public proof-of-concept dropped. Patch now if the API is enabled.
 Security
DuneSlide Turns a Cursor Prompt Into Full Code Execution
Cato AI Labs disclosed DuneSlide, two 9.8-severity flaws (CVE-2026-50548 and CVE-2026-50549) that let a poisoned web page or MCP response escape Cursor's AI sandbox and run any command on a developer's machine, no click required.
 Security
A PraisonAI Flaw Was Exploited Within Hours of Disclosure
Attackers began hitting the PraisonAI authentication-bypass flaw, CVE-2026-44338, less than four hours after it was publicly disclosed, because a legacy Flask API server shipped with authentication disabled by default.
 Security
A 9.8 Oracle E-Business Suite Flaw Is Under Active Attack
CVE-2026-46817, a 9.8-severity unauthenticated takeover flaw in Oracle E-Business Suite's Payments module, is being exploited in the wild, first seen June 27, 2026, six weeks after a patch and before any public exploit existed.
 Security
BlueHammer Defender Zero-Day Hit SYSTEM in the Wild
CVE-2026-33825, nicknamed BlueHammer, is a Microsoft Defender flaw that let a low-privileged attacker win SYSTEM by racing Defender's own rollback engine; it was exploited in the wild and later tied to ransomware.
 Security
FortiBleed Exposed Credentials for 86,000 Fortinet Firewalls
FortiBleed leaked working admin credentials for roughly 86,000 internet-facing Fortinet firewalls across 194 countries. Because it exploits no software bug, there is nothing to patch: every affected organization must treat its credentials as compromised.
 Security
A Cisco Zero-Day Was Exploited for Two Months Before Anyone Knew
Mandiant found that CVE-2026-20245, a high-severity Cisco Catalyst SD-WAN flaw, was exploited as a zero-day at least two months before Cisco disclosed it on June 4, 2026. Patches began rolling out June 10, after attackers already had a long head start.
 Security
Microsoft Just Shipped Its Largest Patch Tuesday Ever, and That Is Not Good News
June 2026 was the most patch-dense month in Microsoft history: 200 vulnerabilities in one Patch Tuesday, including six zero-days. A record like this is a symptom, not an achievement.
 Security
A Self-Spreading Worm Is Eating the Open-Source Supply Chain. Its Name Is Shai-Hulud.
A self-propagating worm has compromised over 100 npm and PyPI packages in a single June wave, stealing developer credentials and using them to infect more packages. The source code is now public, and clones have arrived.
 Security
An Anonymous Account Is Dumping Zero-Days Into the Open. That Should Worry Everyone.
An anonymous GitHub account is mass-publishing working exploits for flaws vendors never got to patch. It is a direct attack on the fragile bargain that keeps software security from becoming a free-for-all.
 Security
Passkeys Are Killing the Password, Finally
After decades of failed attempts to replace the password, a standard called passkeys is actually gaining ground. The reason is that it removes the part humans get wrong.
 Security
Why 'Zero Trust' Is More Than a Buzzword
The phrase gets stamped on every security product, which makes it easy to dismiss. The idea underneath is a genuine and overdue shift in how networks are defended.