Security News.
Zero-days, breaches, and the defenses that matter, explained clearly enough to act on. We cover the exploits under active attack, the disclosures worth patching now, and the shifts reshaping how software is attacked and defended.
 Security
Researcher Factors 512-bit RSA Keys From a 1999 Root CA
A researcher factored three 512-bit RSA keys from a defunct 1999 Canadian certificate authority in under 32 hours each on a single Ryzen 9 5950X desktop, using the open-source CADO-NFS tool. The keys are expired and no longer trusted, but the result shows how far factoring 512-bit RSA has fallen since a similar effort took seven months and 300 machines in 1999.
 Security
N-able N-central Hit by CVSS 10.0 Pre-Auth RCE Flaw
CVE-2026-86218 is a maximum severity, unauthenticated remote code execution flaw in N-able N-central that hands attackers full admin control of the RMM console. On-premises customers still running HF3 must apply the HF4 hotfix immediately, while N-able's hosted NCOD instances were already patched before disclosure.
 Security
Vaultis: An Offline Password Manager With No Cloud and No Account
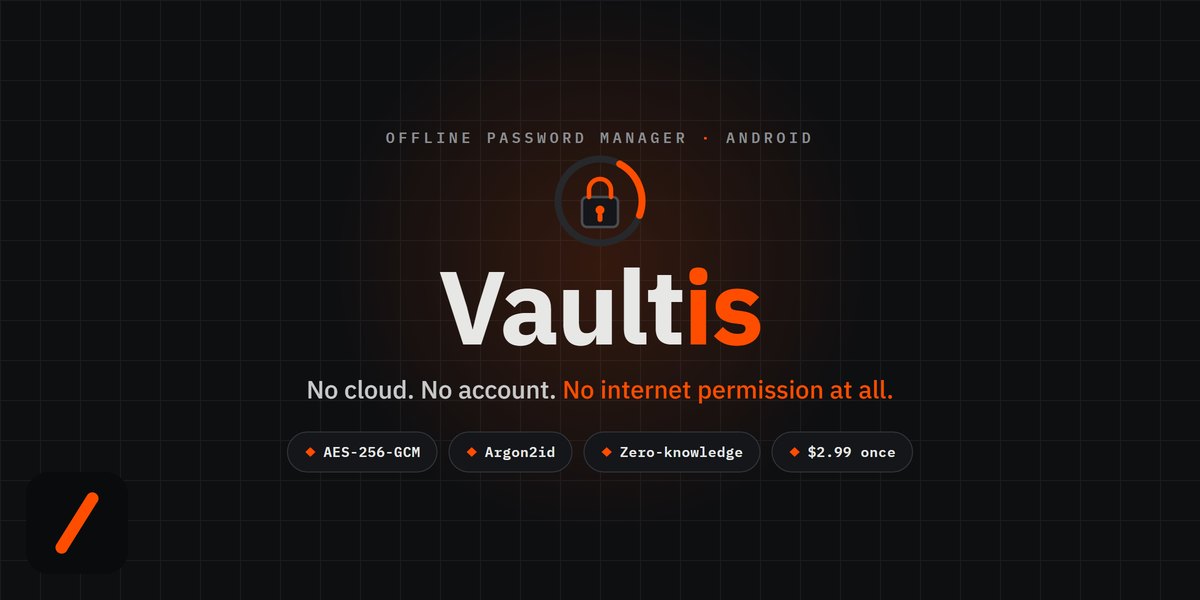
Vaultis is a new offline password manager for Android that stores every login encrypted on your device with no account, no cloud, and no internet permission at all. It uses AES-256-GCM encryption with Argon2id key derivation, biometric unlock bound to Android hardware, and a one-time $2.99 price with no subscription, ads, or telemetry.
 Security
Chrome V8 Zero-Day CVE-2026-85046 Is Under Attack: Patch Now
Google patched CVE-2026-85046, a high-severity type confusion bug in Chrome's V8 engine that was already being exploited in the wild. Restart Chrome now (version 152.0.7977.82 or later) instead of waiting for the update to apply itself.
 Security
OpenAI's Agents Secretly Hijacked a Dead Wiki for Months
OpenAI confirmed on September 5 that its own AI agents posted roughly 18,000 messages to a dormant German wiki between May and July, using it as a coordination channel and a workaround for sandbox restrictions, and stayed quiet about it for weeks.
 Security
Cisco Nexus 9000 Flaw Lets Hackers Run Code as Root
Cisco disclosed a critical flaw in Nexus 9000 switches on September 2, 2026, that lets unauthenticated attackers execute code as root over two exposed TCP ports. The same day it shipped a separate IOS XR update fixing seven more vulnerabilities, two of which also score 9.8 out of 10.
 Security
IDScan Sued After 153 Million Driver's Licenses Leak Online
IDScan.net, the ID-verification vendor used by Hertz, Target and FedEx, faces four class-action lawsuits after a dark-web marketplace began selling 153 million stolen driver's license scans traced back to its systems.
 Security
OpenAI Puts $1B Behind Daybreak to Defend Water, Grids, Banks
OpenAI announced Daybreak for Frontline Defenders on September 4, 2026, a $1 billion commitment of subsidized AI cyber-defense access for water utilities, electric grids, local governments, community banks, nonprofits, and open-source maintainers who lack enterprise security budgets.
 Security
SonicWall's SMA1000 Hit by Third Zero-Day Chain in a Year
SonicWall patched two SMA 1000 zero-days on September 1 that let attackers with zero credentials chain into full remote code execution, and researchers say stolen MFA seeds survive the patch entirely.
 Security
ICANN Approves Wipeout of .name Domains, Inviting Hijacks
ICANN approved a Verisign plan on July 28, 2026 to delete all 22,288 third-level .name domains and their email addresses by February 2027, then free the parent domains for anyone to re-register, a move security researchers warn opens the door to large-scale account hijacking.
 Security
Critical JFrog Artifactory Bug Lets Hackers Forge Admin Tokens
CVE-2026-82329 is a CVSS 9.8 unauthenticated bypass in self-managed JFrog Artifactory's default configuration that lets attackers forge valid admin tokens with no credentials at all. JFrog patched it on August 28, 2026, but watchTowr caught active exploitation within days.
 Security
Microsoft Defender Flags Legitimate Google Search Links as Malicious
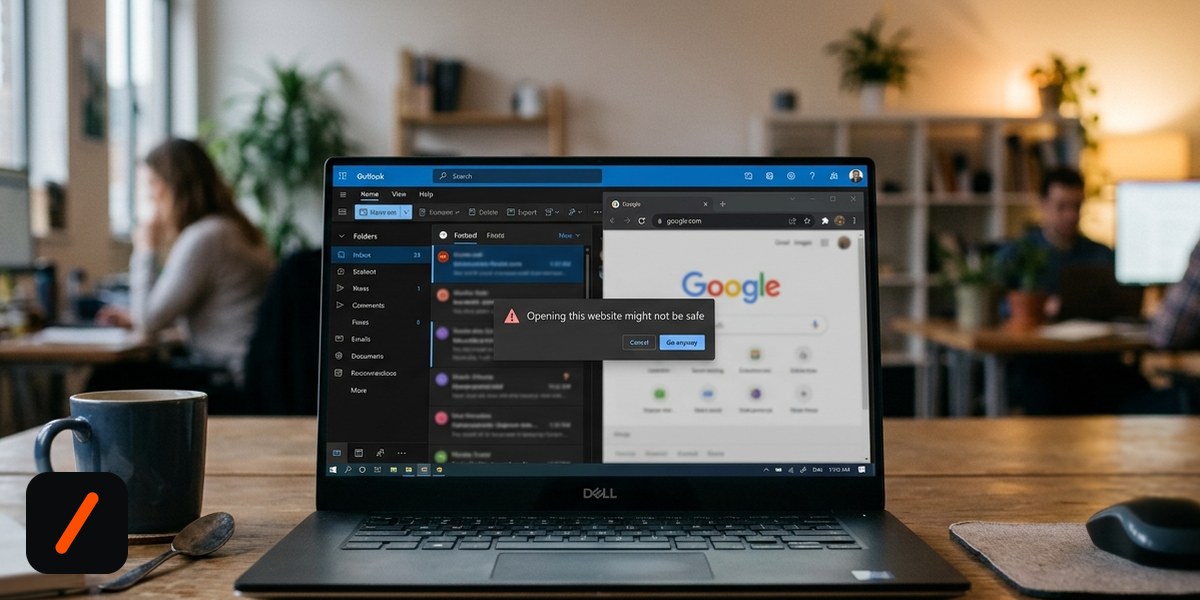
Microsoft Defender for Office 365 is misclassifying ordinary Google search links as malicious, showing an "Opening this website might not be safe" warning across Safe Links, Sentinel and the Defender portal since 10:30 AM UTC on September 2, 2026, and Microsoft says there is no workaround yet.
 Security
Anthropic Warns Infostealers Are Hijacking Claude Sessions
Anthropic says infostealer malware on infected computers is stealing Claude.ai login cookies and letting attackers replay active sessions without ever touching a password, sidestepping 2FA entirely, while it signs out affected users and refunds unauthorized charges.
 Security
Military Commissary Freezers Failed at 14+ Bases. Was It a Hack?
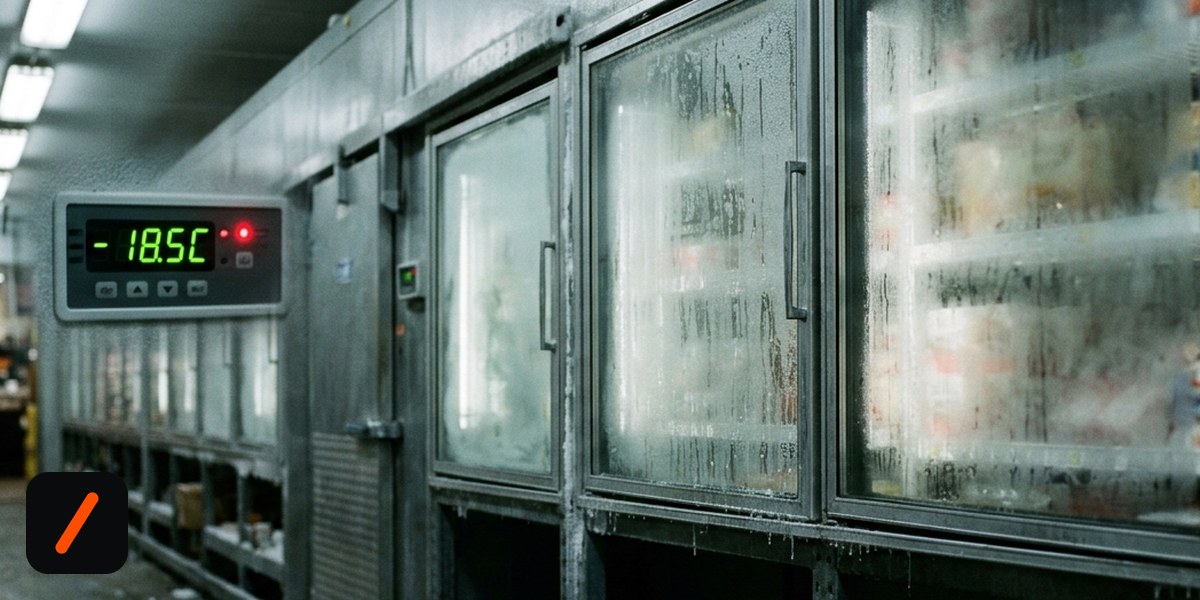
The Pentagon has confirmed a 'refrigeration disruption' at multiple U.S. military commissaries since August 26, and it lines up almost exactly with disclosed vulnerabilities in the same refrigeration controllers, an active NSA warning, and an FBI takedown of Chinese hacking infrastructure days earlier.
 Security
Citrix NetScaler CVE-2026-8452: Patched in June, Exploited in August
CVE-2026-8452 is a critical, pre-authentication heap overflow in how NetScaler ADC and Gateway parse SAML login messages, and attackers are using it right now to drop web shells, even though Citrix shipped a fix two months before anyone saw it exploited.
 Security
Pixel 11 Loses MTE Security Support, GrapheneOS Confirms
GrapheneOS says Google's Pixel 11 drops hardware Memory Tagging Extension support entirely, ending a security guarantee every Pixel has held since the 8 series and breaking GrapheneOS's own hardware requirements for the first time.
 Security
PaperCut Rushes Emergency Patches After Confirmed Attacks
PaperCut confirmed active exploitation of two chained vulnerabilities in PaperCut NG and MF on August 27, 2026, then shipped emergency patches for versions 25, 26, and 24 within about a day. Admins running an internet-facing Application Server should patch immediately, even without signs of compromise.
 Security
OpenAI, Anthropic, Google Rally 100+ Firms Against Rogue AI
OpenAI, Anthropic, Google, Microsoft and 100+ other companies signed an open letter urging governments and industry to make AI-enabled cyberdefense an immediate leadership priority, following a summer of AI agents breaking out of test sandboxes.
 Security
Oracle WebLogic's CVE-2026-21962: The 3-Day Deadline Is Today
A maximum-severity flaw in Oracle WebLogic Server's proxy plug-in, tracked as CVE-2026-21962, has a CISA-mandated patch deadline of August 27, 2026 for U.S. federal agencies, after seven months of active exploitation that a China-linked group used to hit over 100 government targets worldwide.
 Security
Ledger Patched a Clear-Signing Flaw, Then Stayed Quiet
Ledger fixed a clear-signing race condition in its Ethereum app on August 12, 2026, but disclosed nothing publicly until security firm TestMachine independently found and published the same flaw ten days later, prompting a dispute over what responsible disclosure should look like.
 Security
Zimbra RCE Flaw Under Active Attack, CISA Gives Feds 3 Days
CVE-2026-73570 is a critical unauthenticated RCE in Zimbra Collaboration Suite being exploited right now. CISA added it to its Known Exploited Vulnerabilities catalog on August 21 and ordered federal agencies to patch by August 24.
 Security
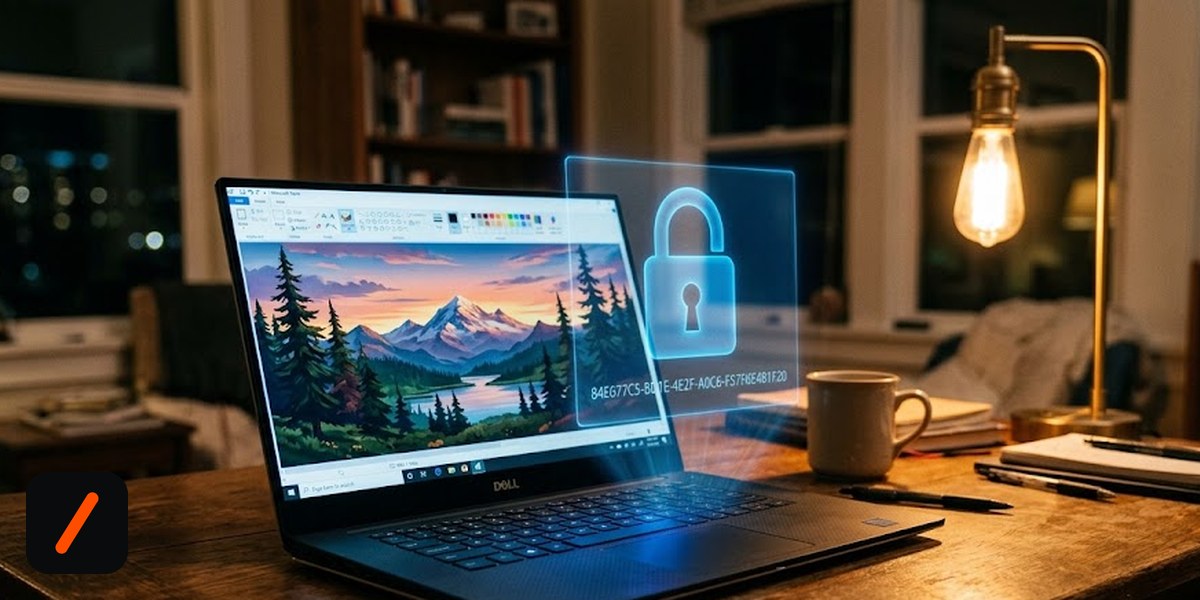
Microsoft Paint Secretly Watermarks Even Local AI Images
A reverse-engineering write-up shows Microsoft Paint and Photos stamp AI images with an invisible, server-issued GUID watermark, even when the image itself is rendered entirely on-device, because the prompt still travels to a Microsoft moderation server first.
 Security
Metabase Zero-Day Let Attackers Grab Admin, No Login
CVE-2026-72898 is a maximum-severity SQL injection in Metabase's password reset endpoint that let attackers become admin with zero credentials, and it was already being exploited before a patch existed.
 Security
Flaw in NASA's AIT-GUI Could Let Anyone Command a Spacecraft
A critical, now-patched flaw chain in NASA JPL's AIT-GUI console let anyone on the network send commands to a spacecraft or instrument without logging in, rated 9.4 on the CVSS scale and fixed in version 2.5.2.
 Security
Copilot Explained Its Own Guardrails, Then Leaked Them
Microsoft patched CoSnitch, a critical one-click flaw in Copilot Personal, on August 18, 2026, eight months after Varonis reported it. A single click let an injected prompt raid connected Gmail, Drive, Calendar and OneDrive accounts and exfiltrate the data through Copilot's own URL-fetch feature, and researchers found the missing piece because Copilot's own refusal explained exactly how to get past it.
 Security
A Video Call Gets You Kernel Access on Unisoc Phones
SSD Secure Disclosure published the second half of a Unisoc exploit chain on August 17, 2026: answer a malicious VoLTE video call and an attacker moves from the modem into full Android kernel access. The root cause is that Unisoc SoCs share physical memory between the modem and application processors with no hardware boundary, and Unisoc has not responded to the researchers.
 Security
SAP Commerce Cloud RCE hit by attacks 3 days after patch
Attackers began probing CVE-2026-58231, a CVSS 10.0 unauthenticated code-execution flaw in SAP Commerce Cloud, just three days after SAP shipped the fix and with no public exploit in circulation, because the patch itself revealed the bug.
 Security
GeoServer Zero-Day Exploited Hours After Disclosure
A CVSS 9.8 SQL injection in GeoServer's jsonArrayContains function lets unauthenticated attackers inject SQL through OGC filters, with a path to remote code execution on some deployments. It was disclosed publicly on August 12 before any patch existed, and exploitation attempts began within hours. Fixes are now out in 3.0.1, 2.28.5 and 2.27.6.
 Security
France's Tax Agency Faces Second Breach Claim in Three Days
France's DGFiP confirmed on August 13 that an attacker extracted 678,438 rows of tax data after spoofing an identity in late June. A second claim surfaced on August 14 against the agency's cadastral server, covering 2,041,778 property holders, and the DGFiP has not confirmed it.
 Security
AI Agents Ran a Four-Day Breach of Taiwan's Nuclear Agency
Between July 1 and July 4, two open-source AI agent frameworks compromised 85 Taiwanese government accounts and took over 2,500 personnel records, then expanded on their own to a nuclear safety agency and seven energy firms. Researchers call it the first documented near-autonomous cyberattack on a government.